The Big Question
APIs are not just another attack surface. They are the attack surface.
Every mobile app, every SaaS product, every microservice, and every third-party integration communicates through APIs. They expose your business logic and data directly, often with less UI-layer friction than traditional web pages . And attackers have noticed.
Akamai's 2026 API Security Impact Survey found that 87% of organizations globally experienced an API security incident in the past 12 months, up from 76% in 2022. In India, the figure is even higher 93% . The financial toll has more than doubled year-over-year, with the average cost per incident exceeding **US$1 million** in APAC, up sharply from US$580,000 last year .
The root causes are consistent and predictable. CERT-In data shows a 62% increase in API attacks on the Indian financial sector, with 57% caused by security misconfiguration . The OWASP API Security Project reports that three of the top five API risks are authorization-related . In other words, most breaches aren't exotic exploits. They're missing or wrong access-control checks on endpoints that otherwise work fine .
The visibility gap makes everything worse. Only 23% of organizations can fully list their API assets and identify which ones expose sensitive data down from 40% in 2022 . You cannot secure what you cannot see.
Cost Based on Application Type
API security costs vary dramatically based on your application's exposure, data sensitivity, and regulatory requirements. There is no single price tag only a range of investments that scale with risk.
| Application Type | Typical Annual Security Investment | What It Covers |
|---|---|---|
| Internal Enterprise API | ₹3,00,000 – ₹12,00,000 | Gateway controls, authentication, basic monitoring |
| Customer-Facing Web App | ₹12,00,000 – ₹40,00,000 | WAF, API gateway, rate limiting, schema validation, observability |
| Mobile-First Application | ₹20,00,000 – ₹60,00,000 | All above plus certificate pinning, runtime protection, secret removal |
| Financial / Healthcare API | ₹50,00,000 – ₹2,00,00,000+ | Full OWASP coverage, compliance auditing, dedicated security team, continuous testing |
The hidden cost trap: Most organizations underestimate the ongoing operational cost of API security by 40-60%. A gateway deployment is a one-time cost. But schema maintenance, policy tuning, monitoring, and incident response are continuous expenses. Gartner's research shows that 92% of businesses implementing agentic AI experience cost overruns, with 71% lacking control and visibility into cost drivers .
For Indian enterprises subject to CERT-In mandates, additional compliance costs apply: 6-hour incident reporting, 180-day log retention, and annual cybersecurity audits aligned with ISO 27001 . These are not optional.
Breakdown by Defense Layer
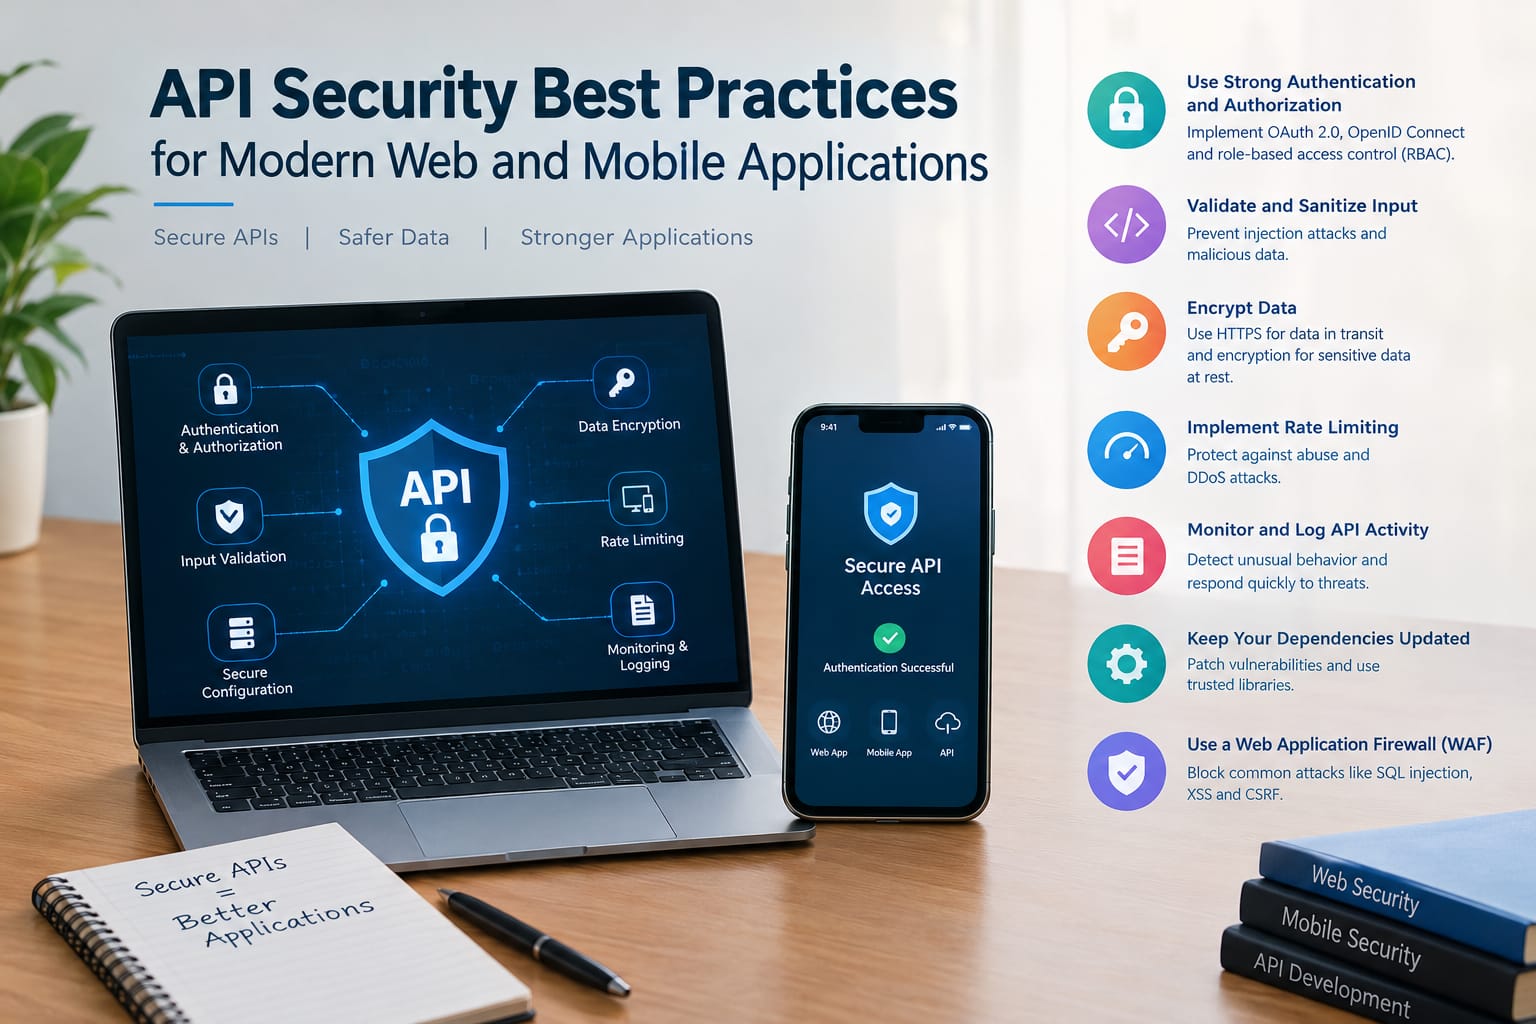
API security is not a single control. It is a layered architecture where each layer addresses specific risks. Here's the 2026 practical baseline:
| Defense Layer | Implementation Cost | Ongoing Cost | Primary Risk Addressed |
|---|---|---|---|
| API Gateway (auth, rate limiting) | ₹5,00,000 – ₹15,00,000 | ₹1,00,000 – ₹3,00,000/yr | Broken auth, resource consumption |
| Schema Validation (OpenAPI/JSON) | ₹2,00,000 – ₹6,00,000 | ₹50,000 – ₹1,50,000/yr | Injection, mass assignment, malformed input |
| Object-Level Authorization | ₹3,00,000 – ₹8,00,000 | ₹75,000 – ₹2,00,000/yr | BOLA (API1), property-level auth (API3) |
| Bot Detection & Behavioral Analysis | ₹4,00,000 – ₹12,00,000 | ₹1,50,000 – ₹4,00,000/yr | Credential stuffing, scraping, automation |
| Monitoring & Observability | ₹2,00,000 – ₹6,00,000 | ₹80,000 – ₹2,50,000/yr | Anomaly detection, incident response |
| Secret Management (Zero Secrets) | ₹2,00,000 – ₹5,00,000 | ₹60,000 – ₹1,50,000/yr | Credential theft, API key extraction |
The critical insight: The most expensive layers are not the ones most organizations prioritize. Schema validation and object-level authorization cost a fraction of bot detection, but they address the vulnerabilities that top the OWASP list . A gateway that enforces documented schemas would have rejected the payloads that caused real-world prototype pollution attacks in three downstream services .
Breakdown by Developer Type (2020-2026)
API security requires specialized skills that most internal teams don't have. The Indian talent market offers both opportunity and risk:
| Developer Type | Hourly Rate (India) | Typical Engagement | What They Deliver |
|---|---|---|---|
| Freelancer | ₹1,000 – ₹3,000 | ₹25,000 – ₹75,000 | Basic gateway configuration, SSL setup |
| Small Security Firm | ₹2,500 – ₹6,000 | ₹1,50,000 – ₹5,00,000 | Auth implementation, rate limiting, basic monitoring |
| Mid-Size Integrator | ₹6,000 – ₹12,000 | ₹5,00,000 – ₹25,00,000 | Full OWASP coverage, custom policy engines |
| Enterprise Security Consultancy | ₹12,000 – ₹20,000+ | ₹25,00,000+ | Compliance-driven architecture, continuous testing |
India's structural advantage: Security engineers with comparable certifications bill at 60-80% less than US rates. But API security specifically requires experience with API gateways (Kong, Apigee, AWS API Gateway), schema tools (OpenAPI, JSON Schema), and identity platforms (OAuth 2.0, OIDC). The critical question before hiring: "Show me an API security deployment you completed in the last 12 months not a design document, a live production environment with real traffic."
Why Prices Changed in 2026
Three forces have reshaped API security economics.
First, AI adoption exploded the attack surface. 42% of security professionals report that APIs powering AI applications, agents, and LLMs were targeted in the past 12 months . AI-generated code accelerates API deployment, but security foundations haven't kept pace. Only 19% of organizations say security testing is fully embedded across the API software development life cycle and CI/CD pipeline .
Second, behavioral analytics stopped working as a boundary. For years, defenders relied on patterns of touch, scroll velocity, and navigation sequences to distinguish humans from bots. Agentic AI invalidated that premise. A modern agent can drive a real device, generate plausible sensor traces, and pace its actions to look entirely human . Behavioral signals retain narrow utility for detecting unsophisticated bots, but they are no longer a reliable boundary for high-value APIs.
Third, India's regulatory environment tightened. CERT-In's Cyber Security Directions mandate 6-hour incident reporting, 180-day log retention, and KYC for service providers . The DPDP Act requires Data Fiduciaries to obtain informed consent before processing personal data, with APIs often serving as the consent mechanism . Non-compliance penalties are severe.
The result: API security is more necessary than ever, and more expensive to implement poorly.
Pro Tips to Save Money in 2026
1. Flip the default to deny. Every route requires authentication unless explicitly carved out. The gateways that produce the most incidents are the ones where the implicit default is open and individual routes are protected by per-route policies . Anything public login endpoints, health checks, marketing pages gets an explicit public marker that shows up in audit logs.
2. Implement object-level authorization on every endpoint. BOLA has topped the OWASP API list since 2019 and remains the most exploited vulnerability . Never trust client-supplied IDs. Always validate ownership server-side. Use indirect references (UUIDs, tokens) instead of sequential integers. This is the single highest-impact control you can implement .
3. Deploy schema validation at the gateway. OpenAPI or GraphQL schema enforcement catches a meaningful share of injection and mass-assignment vulnerabilities before they reach the backend. But beware: a schema that is generated once and left stale produces worse outcomes than no schema validation, because it creates false confidence. Bake schema generation into your API release process .
4. Layer your rate limits. Rate limiting at the gateway does two distinct jobs: protecting backends from accidental overload and slowing credential stuffing. These need different limits. Backend protection limits are per-API-key and sized to capacity (100-1000 RPS). Attack-mitigation limits are per-IP or per-token and sized much lower (10-50 RPS) .
5. Remove secrets from mobile apps. A secret that exists on the device is a secret that will be extracted. Static analysis recovers obfuscated strings, dynamic analysis captures them at use, and memory inspection extracts them from the heap. The only durable defense is for the secret not to be there in the first place .
6. Build observability without leaking credentials. Gateway logs are gold for incident response and a hazard for compliance. Use structured logging with explicit allowlists for captured fields. Redact authorization headers, API keys, and cookies by default. Sample bodies at low rates with active PII detection .
Questions to Ask Before Hiring
Before you commit budget to any API security engagement, ask these questions.
1. "Can you produce a complete API inventory every endpoint, version, auth requirement, and data classification?" Only 23% of organizations have this. If your partner can't build it, they can't secure your APIs .
2. "How do you handle object-level authorization on every endpoint?" BOLA is the #1 API risk. The right answer involves server-side ownership validation on every resource access, not client-side UI hiding .
3. "What's your schema validation strategy, and how does the schema stay in sync with the code?" A stale schema is worse than no schema. Ask for continuous integration between API releases and schema updates .
4. "How do you test for API attacks that don't look like attacks?" Credential stuffing, scraping, and business flow abuse often appear as legitimate traffic. Ask for behavioral analysis, rate limiting layered by purpose, and bot detection .
5. "Who maintains the security posture after deployment?" API security is not a one-time project. Ask for retained operations, monitoring, and policy tuning as part of the engagement.
Why Delhi is a Great Hub for API Security
Delhi-NCR has become a serious destination for API security work, and the reason isn't just cost.
The region hosts a dense cluster of fintech, ecommerce, and government digital infrastructure the exact sectors facing the highest API attack volumes. CERT-In's data shows a 62% increase in API attacks on the Indian financial sector, and Delhi is the center of India's financial services ecosystem .
India's regulatory environment is also driving demand. CERT-In's Cyber Security Directions apply to all organizations, and the DPDP Act requires consent-driven data processing where APIs often serve as the mechanism . Organizations in Delhi are actively building compliance-aligned API security architectures because they have no choice.
The talent density keeps improving. With a steady pipeline of security engineers, API gateway specialists, and cloud architects, Delhi offers a combination of cost and capability that's hard to match. And the time zone advantage matters: a Delhi-based team can sync with Middle East morning, European afternoon, and US East Coast evening.
What We Offer
At Innovative AI Solutions, we treat API security as an engineering discipline, not a compliance checkbox.
Our approach:
-
API Inventory First. We map every endpoint, version, auth requirement, and data classification. You cannot secure what you haven't inventoried.
-
Object-Level Authorization. We implement server-side ownership validation on every resource access. BOLA addressed at the architecture level.
-
Schema Validation by Default. OpenAPI schemas enforced at the gateway, kept in sync with every API release. Malformed requests rejected before they reach your backend.
-
Layered Rate Limiting. Separate policies for backend protection and attack mitigation. Credential stuffing slowed without blocking legitimate traffic.
-
Zero Secrets Architecture. No API keys, tokens, or credentials embedded in mobile apps. Secrets managed server-side, rotated from a single control plane.
-
Continuous Monitoring. Structured logging, anomaly detection, and incident response playbooks aligned with CERT-In's 6-hour reporting mandate.
Our principle is simple: small steps, fast iteration, data speaks.
Frequently Asked Questions
Q: What is the OWASP API Security Top 10?
The OWASP API Security Project maintains a list of the most critical API security risks. The 2023 edition includes: Broken Object Level Authorization (API1), Broken Authentication (API2), Broken Object Property Level Authorization (API3), Unrestricted Resource Consumption (API4), Broken Function Level Authorization (API5), Unrestricted Access to Sensitive Business Flows (API6), Server-Side Request Forgery (API7), Security Misconfiguration (API8), Improper Inventory Management (API9), and Unsafe Consumption of APIs (API10) .
Q: Why is BOLA so dangerous?
Broken Object Level Authorization has topped the OWASP API list since 2019 because it's trivial to exploit and devastating at scale. An endpoint like authenticates the caller but doesn't check that order 1043 belongs to them. Change the ID to 1044 and you read someone else's order . The fix is discipline: every request that references a resource must verify the authenticated user is authorized for that specific resource, server-side, on every endpoint.
Q: How much does API security cost in India?
For an internal enterprise API, annual security investment runs ₹3,00,000 to ₹12,00,000. For customer-facing web apps, it's ₹12,00,000 to ₹40,00,000. For financial or healthcare APIs, ₹50,00,000 to ₹2,00,00,000+ .
Q: Can I just use a WAF and call it done?
No. A WAF blocks many known web attack patterns, but APIs fail in specific ways that a WAF was never designed to address. Excessive request rates, abusive automation, malformed payloads, and attacks directed at business-critical endpoints require controls that extend beyond signature-based inspection . You need gateway controls, bot mitigation, rate limiting, and observability alongside the WAF.
Q: What is CERT-In's role in API security?
CERT-In (Indian Computer Emergency Response Team) issued Cyber Security Directions that mandate 6-hour incident reporting, 180-day log retention, synchronized system clocks, and KYC for service providers. API security directly supports compliance through logging, monitoring, incident detection, and secure-by-design .
Frequently Asked Questions (Extended)
Q: How do I test for SSRF vulnerabilities?
Find every parameter that accepts a URL, file path, hostname, or webhook destination. Test internal targets: 127.0.0.1, 10.x.x.x, and 169.254.169.254 (cloud metadata). Test non-HTTP schemes: file://, gopher://, ftp://. Use DNS callbacks to detect blind SSRF. Validate webhook URLs against an explicit allowlist only .
Q: What's the biggest mistake companies make with API security?
Treating it as a one-time project. API security requires continuous schema maintenance, policy tuning, monitoring, and incident response. A gateway deployment without ongoing ownership will quietly degrade within 90 days.
Q: How do I handle third-party API security?
List every third-party API your app consumes and document the data flow. Validate all third-party responses against an expected schema before processing. Sanitize third-party data for injection before storing or using it. Validate TLS certificates on all outbound connections. Store API keys in a secrets manager, not in code .
Q: What's the first step I should take tomorrow?
Flip your gateway's default to deny. Every route requires authentication unless explicitly carved out. Then implement object-level authorization on your highest-risk endpoints. Those two changes address the most exploited API vulnerabilities, and they cost almost nothing compared to the breach they prevent.
Contact Us:
Phone: +91 7464 099 059 / +91 9689967356
Email: info@innovativeais.com
Address: 9th Floor, Pearls Best Heights-I, Head Office: 904, Netaji Subhash Place, Delhi, 110034